Legal Documentation Required for AI Systems in the USA

A single missing risk assessment cost one Colorado-based SaaS company $47,000 in penalties before its AI hiring tool had been live for six months. That figure is about to look modest. With the Colorado AI Act enforcement beginning in 2026, California’s suite of AI transparency laws now active, and more than 35 states advancing AI-related […]
Who Is Liable When AI Fails? A Legal Breakdown for 2026

Mobley v. Workday holds vendors directly liable. Air Canada pays for chatbot advice. The AI LEAD Act proposes federal product liability. Five theories, four parties, and the governance that determines who pays. The liability landscape is forming: Mobley v. Workday: vendor directly liable for AI discrimination. Air Canada: deployer liable for chatbot advice. Affable: client’s case […]
AI Vendor Due Diligence Checklist for Legal Teams: The Pre-Contract Assessment Guide

97% of AI-breached organizations lacked access controls. Supply chain attacks cost $4.91M average. Traditional assessment misses model-specific risks. Here is the 8-domain checklist legal teams need before signing. The AI vendor risk gap: 13% of organizations reported AI breaches (IBM 2025). 97% of those lacked proper AI access controls. Supply chain compromise: $4.91M average cost. 47% […]
AI Risk Assessments: What Lawyers Should Review Before Signing Off

Colorado requires annual impact assessments retained for 3 years. The rebuttable presumption of reasonable care depends on assessment quality. Here are the 10 elements that determine whether the assessment is your shield or their evidence. The assessment is a legal document: Colorado: annual impact assessments, 3-year retention, producible to AG within 90 days. Rebuttable presumption of […]
AI Contract Clauses Every Lawyer Should Use: The Drafting Guide for 2026

Only 17% of AI contracts include documentation warranties vs. 42% in standard SaaS. Most MSAs don’t address output liability, training data rights, or disgorgement risk. Here are the 12 clauses that close the gaps. The contractual gap: Stanford CodeX: 17% of AI contracts include documentation warranties (vs. 42% SaaS). Most AI vendor agreements shift compliance to […]
AI Vendor Due Diligence Checklist for Legal Teams: The Pre-Contract Assessment Guide

97% of AI-breached organizations lacked access controls. Supply chain attacks cost $4.91M average. Traditional assessment misses model-specific risks. Here is the 8-domain checklist legal teams need before signing. The AI vendor risk gap: 13% of organizations reported AI breaches (IBM 2025). 97% of those lacked proper AI access controls. Supply chain compromise: $4.91M average cost. 47% […]
Global AI Regulation for Lawyers: One Program, Eight Jurisdictions, Zero Parallel Compliance Structures

72+ countries, 1,000+ AI policy initiatives, three regulatory philosophies. Here is how to build a single ISO 42001 compliance program serving the EU, U.S., UK, China, India, Brazil, Canada, and Singapore simultaneously. The global fragmentation: 72+ countries with AI initiatives. Three camps: EU hard law, U.S. existing law + state patchwork, Japan/Singapore soft governance. A multinational […]
U.S. AI Governance: What Lawyers Can Actually Enforce Right Now

New York enacted AI safety law on Thursday. The FTC vacated an AI consent order on Sunday. Same week. Opposite directions. Federal pullback does not mean regulatory relief. Here is every enforcement tool that actually works. The enforcement seesaw (December 2025): Thursday: NY Governor signs RAISE Act, first major state AI safety law post-preemption executive order. […]
From GDPR to AI Act: How to Migrate Your Compliance Operations Without Starting Over
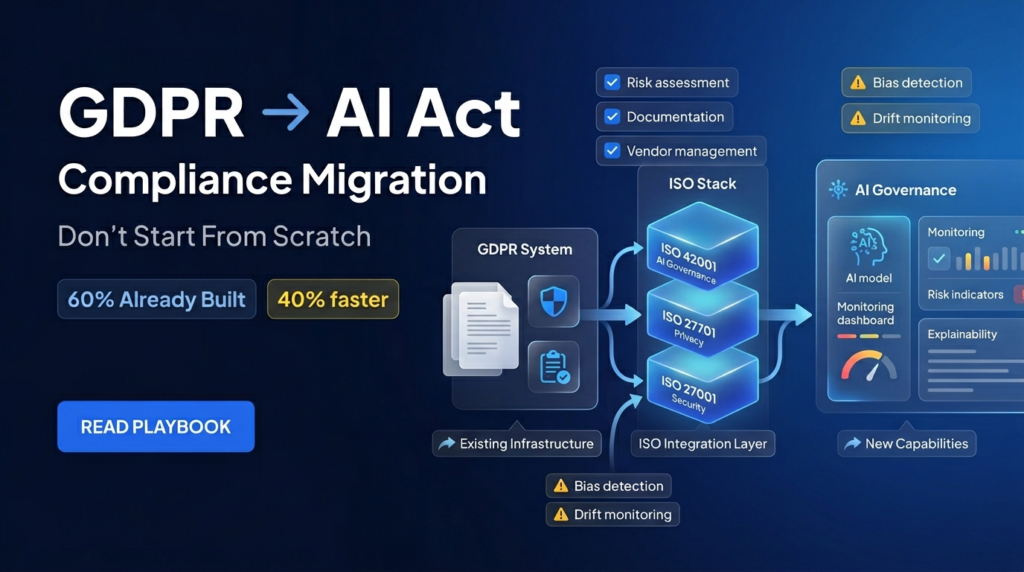
ISO 27001-certified organizations achieve ISO 42001 compliance up to 40% faster. Your GDPR program already built 60% of the infrastructure AI governance needs. Here is the operational migration playbook. The migration advantage: ISO 27001 + ISO 42001 dual certification up to 40% faster than starting from scratch. ISO 27701:2025 now standalone (no longer requires ISO 27001). […]
EU AI Act for U.S. Lawyers: How to Determine Client Scope, Classify Risk, and Build the Compliance Engagement
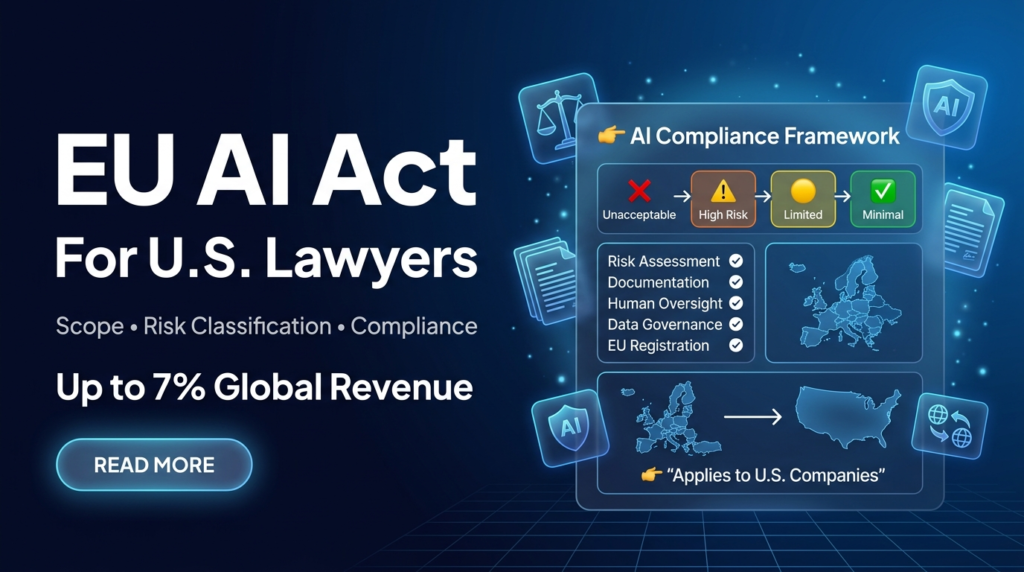
The jurisdictional trigger is use “in the Union,” not corporate domicile. Fines reach 7% of global turnover. High-risk enforcement lands August 2, 2026. Here is the practical playbook for advising U.S. clients with EU exposure. Penalty exposure for U.S. companies: Prohibited AI violations: up to €35M or 7% of global annual turnover. High-risk non-compliance: up to […]