Why AI Governance Is the Next Big Legal Practice Area: The GDPR Playbook Is Repeating
88% of businesses use AI. Only 10% of law firms have governance policies. 1,100+ state AI bills in a single year. The structural conditions that created billion-dollar privacy practices post-GDPR are present, and in several dimensions, more favorable for AI governance. The formation window: AI tool usage among legal professionals surged from 19% (2023) to 79% […]
What Every Lawyer Must Know About AI Risk in 2026: Malpractice, Sanctions, and the Risks You Cannot Delegate
A federal court terminated a client’s entire case because their lawyer filed AI-fabricated citations repeatedly. Over 700 documented hallucination cases. $100K+ sanctions. And a double bind where both AI misuse and failure to use AI create liability. February 2026 precedent: A federal court issued a default judgment against a client, terminating their entire case, because their […]
AI Regulation Is Expanding: Blind Spots Catching U.S. Lawyers Off Guard
70+ AI laws passed in 27 states in a single year. TRAIGA safe harbors nobody discusses. Chatbot companion bills in 11+ states. A 10-year federal moratorium proposal. Privacy laws with AI profiling rights. Here are the regulatory blind spots creating unaddressed client liability. Beyond the headlines: 70+ AI laws in 27 states (2025). 1,100+ bills introduced. […]
AI Model Drift and Performance Risk: Detection, Governance, and What U.S. Organizations Must Monitor
40% of companies experience noticeable AI performance degradation within the first year. Drift produces no error messages, only silently worsening decisions. Here is how to catch it before the business consequences compound. A McKinsey survey found that 40% of companies deploying AI models experienced noticeable performance degradation within the first year due to drift. Unlike […]
AI Data Risk and Privacy Risk Management: A Practical Guide for U.S. Organizations
AI systems memorize training data, leak information through prompts, and infer attributes never explicitly collected. Here is how to manage these risks within the frameworks regulators expect. By the numbers: AI incidents surged 56.4% in 2024 (Stanford AI Index). ~40% of organizations report an AI privacy incident. ~15% of employees have pasted sensitive data into […]
Bias Risk in AI Systems: Sources, Real-World Consequences, and What U.S. Organizations Must Do About It
From the Workday class action to the healthcare algorithm that failed Black patients, AI bias has moved from theoretical concern to boardroom priority. Here is how to identify, measure, and manage it. In May 2025, a federal judge in the Northern District of California allowed a nationwide collective action to proceed against Workday, the HR […]
AI Risk Mitigation Strategies for High-Risk Systems: A Practical Guide for US Organizations
Seventy-three percent of organizations experienced at least one AI-related security incident in 2024, with average remediation costs exceeding $4.5 million per breach. That number sits uncomfortably alongside the fact that AI adoption in business-critical processes has accelerated faster than the governance structures meant to keep it in check. For US organizations deploying high-risk AI systems […]
Third-Party AI Vendor Risk Management: How U.S. Organizations Can Govern What They Don’t Control
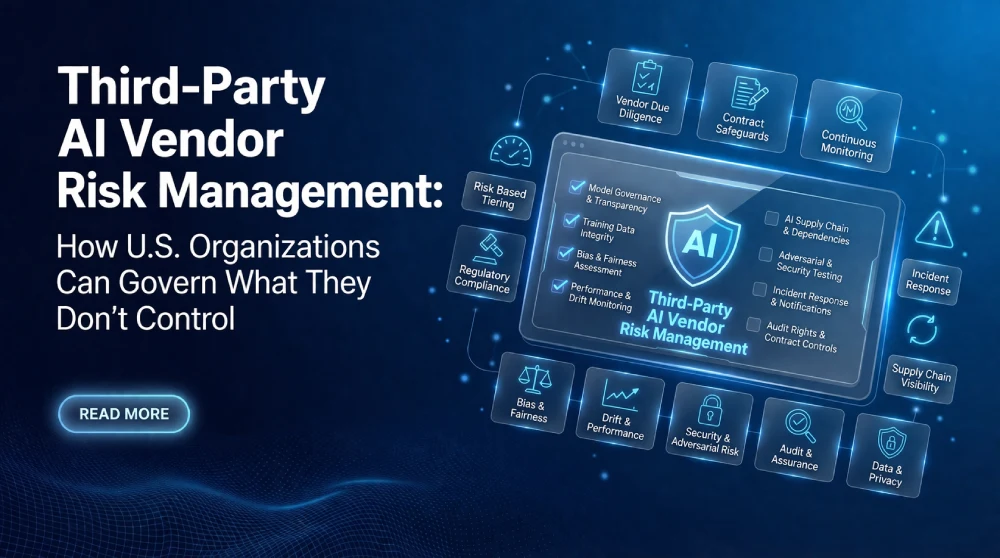
Third-party breach involvement doubled to 30% in a single year. Meanwhile, vendors are embedding AI into their products faster than most organizations can assess it. The governance gap is real, and the liability sits with you. By the numbers: 30% of breaches now involve third parties, doubled from 15% in one year (Verizon 2025 DBIR). […]
Generative AI Risk Management: A Framework for U.S. Organizations Moving from Experimentation to Production
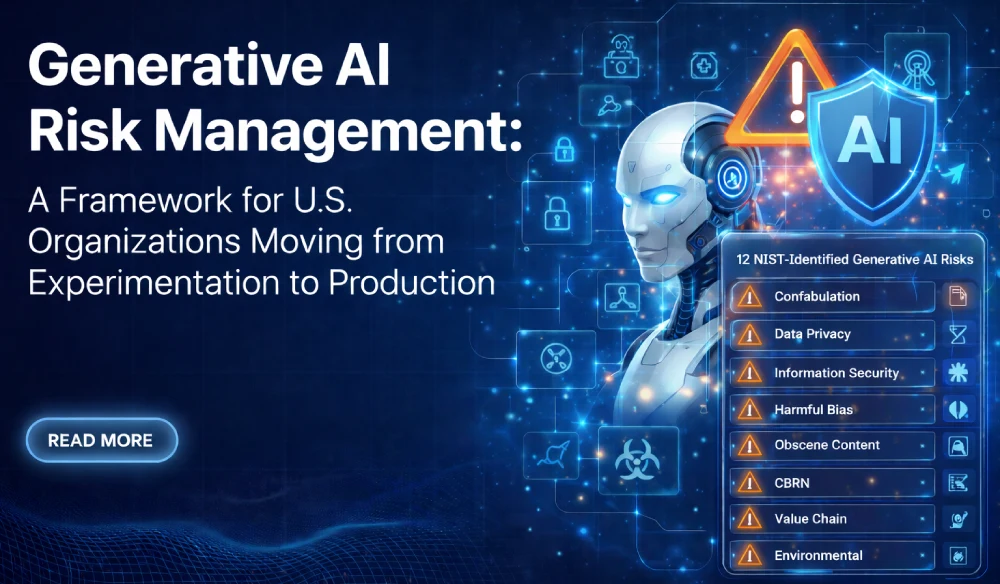
78% of companies use generative AI. Only 19% have governance frameworks. NIST identified 12 risk categories unique to generative systems. Here is how to close the gap between adoption and oversight. The governance gap: 78% of companies use generative AI (McKinsey). 58% have enterprise-wide AI strategies, up from 26% (Info-Tech 2026). Only 19% have fully […]
AI Security Risks and Adversarial Attacks: What U.S. Organizations Face in 2026 and How to Defend Against Them
From prompt injection at 90+ organizations to the fastest breakout time of 27 seconds, the AI threat landscape has moved from research papers to documented compromise. Here is the attack taxonomy and defense playbook. 2025-2026 threat landscape: Adversaries exploited GenAI tools at 90+ organizations via prompt injection (CrowdStrike). eCrime breakout time dropped to 29 minutes, […]